
Systems rarely fail out of nowhere. The reasons are usually there all along, like skipped updates, a backup that was never tested, or a setting no one remembers, all of which compound over time.
“Something broke again, and nobody can tell us why.”
The jobs that are easy to put off, which is usually how the trouble starts.
You'll know what happened and why before we change anything.

We find out what happened. We'll review logs and talk to users, if needed.

We find out why it happened. Logic issue? User error? Third party?

We brief you on the failure and proposed changes to avoid a repeat incident.

We put the changes and procedures in place, then monitor and adjust as needed.
We do the technical work your compliance depends on, and we're clear about where our role ends.
We consult on PCI and help with testing and compliance work.
We're not your cybersecurity consultant or your legal adviser, and we work alongside the people who are, making the changes they ask for.
We align with the NIST Cybersecurity Framework, and we're PCI DSS compliant ourselves, validated each year by self-assessment and each quarter by external vulnerability scans.
This kind of work is never finished.
We maintain systems for years, not only at launch. Neglected long enough, it turns into an expensive deferred maintenance project that grows every quarter.
Three organizations that trusted us with the part no one sees.
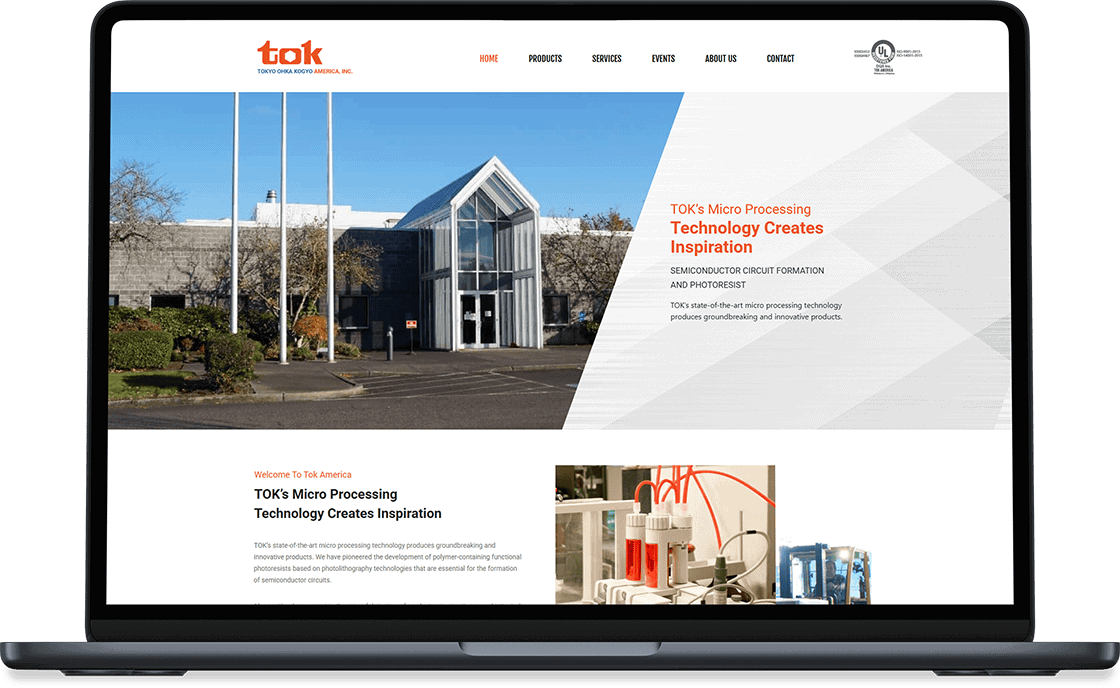
We replaced a manufacturer's ColdFusion sales site with a custom build its own IT staff could keep current, under the parent company's content rules. We also took on its hosting, firewall, and site updates.
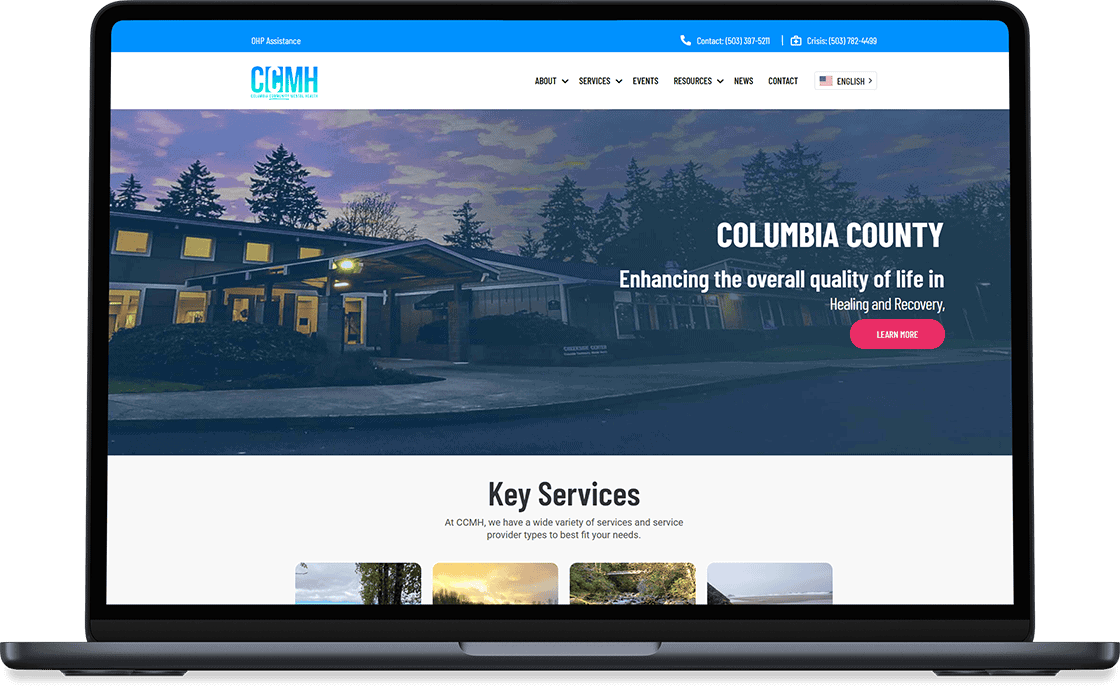
We rebuilt a counseling organization's website around its programs, with contact forms that delivered each message straight to its staff, where not even we could read it.
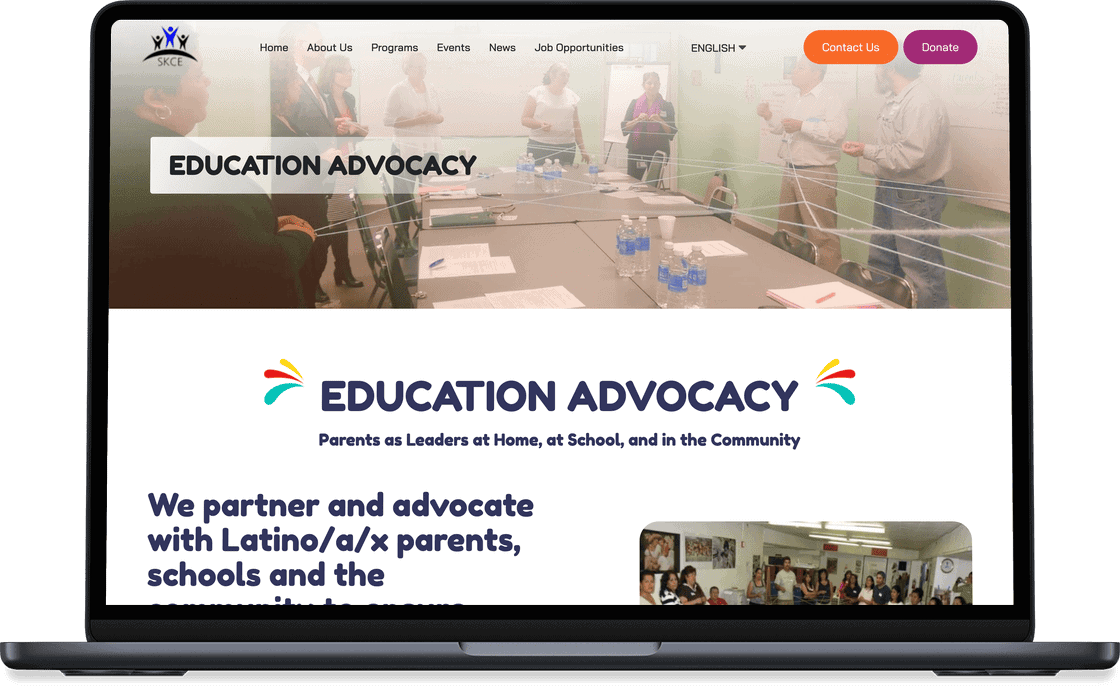
Before redesigning a coalition's bilingual site, we took it over and stabilized it, moving it to new hosting, managing its DNS and email records, and repairing and compressing thousands of images.
Bring us the problem that keeps coming back. We'll start with why.

© 2017 to 2026 IronGlove Studio, LLC. IronGlove Studio® is a registered trademark of IronGlove Studio, LLC.